SEBI CSCRF Incident Reporting: What the FIRE Format Changed
If you are a SEBI-regulated entity, the way you report a cyber incident changed in August 2026 — but not
Practical cyber security guidance for Indian businesses — Zero Trust, SIEM, MDR, endpoint and network security, identity and access management, risk assessments and SOC operations, written by the Novotron security team in Noida.
This is the largest section of the Novotron blog, and it is written for the people who actually have to sign off on security spending: founders, CFOs, IT managers and compliance leads at companies running 20 to 500 endpoints. Every guide here starts from what a mid-sized Indian business really has — a mixed estate of Windows laptops, a firewall someone configured three years ago, Microsoft 365, a few line-of-business servers, and no full-time security engineer — rather than from an enterprise reference architecture that assumes a 24-person SOC.
You will find explainers on the fundamentals (what a firewall does that antivirus cannot, what identity and access management means in practice, how VAPT differs from a compliance audit), buying guides that put real Indian price bands against each service, and operational pieces on running or outsourcing a Security Operations Centre. We cover the threats that are actually hitting Indian SMEs right now — business email compromise, ransomware delivered through unpatched remote access, credential stuffing against Microsoft 365 tenants — and the controls that stop them.
Novotron delivers these services from our office at Aycon Tower, Sector 135, Noida, to clients across Delhi NCR and the rest of India. If a guide raises a question about your own environment, call +91-8130009878 or write to sales@novotrontech.com.
If you are a SEBI-regulated entity, the way you report a cyber incident changed in August 2026 — but not
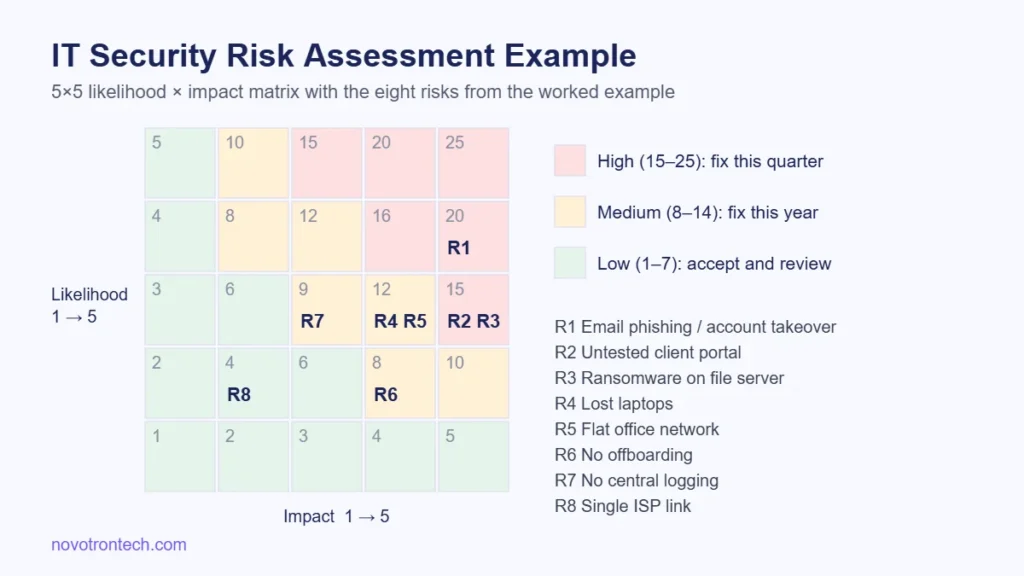
A worked IT security risk assessment example for a 60-person Noida firm: assets, threats, a 5×5 likelihood and impact matrix, the full risk register and the treatment plan.
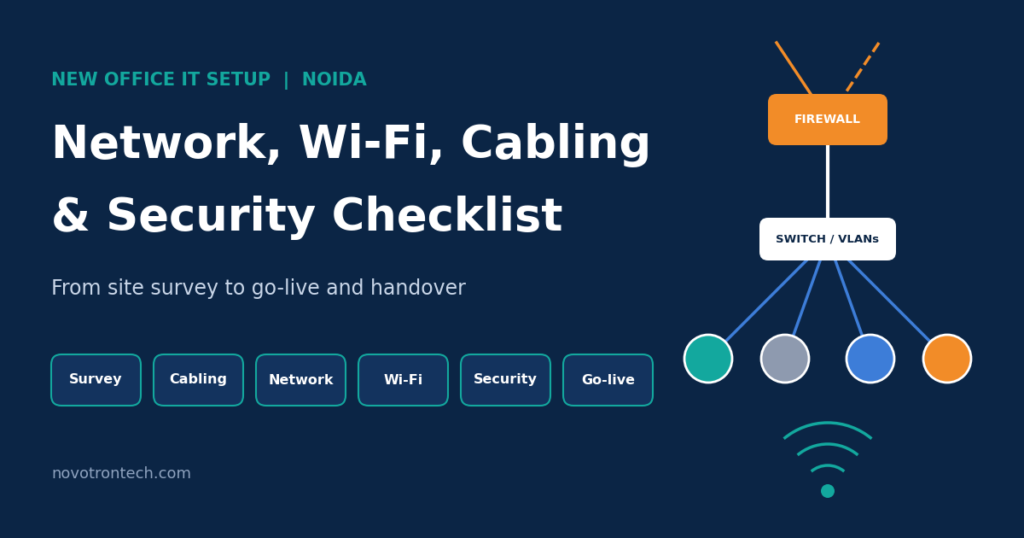
A practitioner’s checklist for setting up IT in a new Noida office: how the network fits together, phased steps from site survey to handover, success metrics, compliance points and common mistakes.
Firewall setup services for FortiGate, Sophos and Palo Alto explained: what a proper configuration includes, how traffic is processed, vendor fit, common mistakes and how to measure success.
A 25-step server hardening checklist for Windows Server and Linux, grouped into identity, network, patching, logging and data layers and mapped to CIS Benchmarks, NIST SP 800-123, ISO 27001 and the CERT-In Directions.
What a real penetration test includes, how the four phases work, what the report and retest must prove, and the six variables that drive the price in Delhi NCR.
What data loss prevention costs in India, where DLP runs, the five-phase rollout that actually finishes, and why block-first projects get switched off.
What a phishing simulation costs in India, how a campaign actually runs, the four metrics that matter, and the mistakes that make simulations backfire.
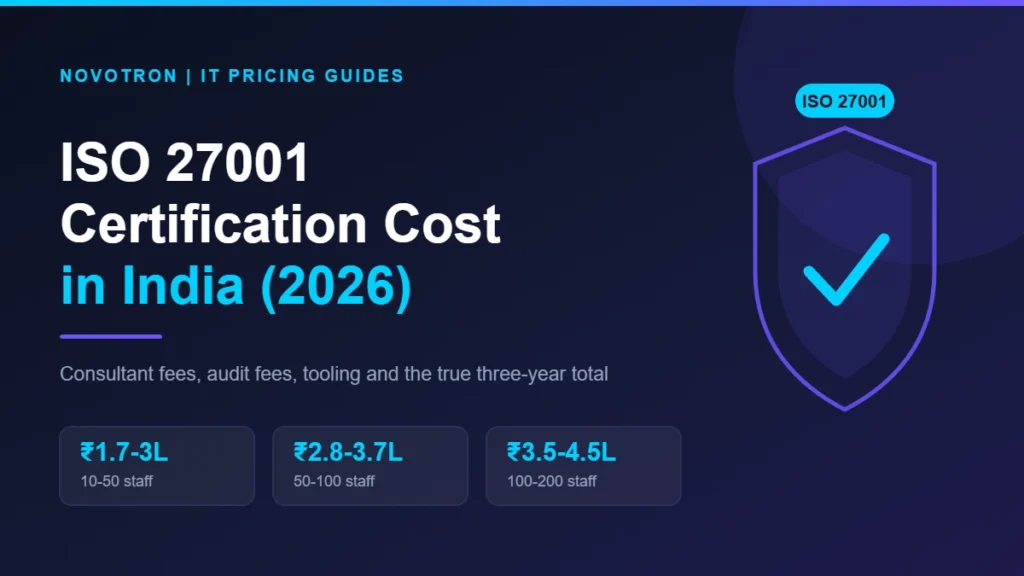
What ISO 27001 certification really costs an Indian company in 2026: consultant fees, audit fees, tooling and the three-year total, with the levers that cut the bill.
How ransomware actually gets in, the controls that stop it in priority order, how to design backups attackers cannot reach, and what the first six hours look like under CERT-In and DPDP reporting rules.