SEBI CSCRF Incident Reporting: What the FIRE Format Changed
If you are a SEBI-regulated entity, the way you report a cyber incident changed in August 2026 — but not
If you are a SEBI-regulated entity, the way you report a cyber incident changed in August 2026 — but not
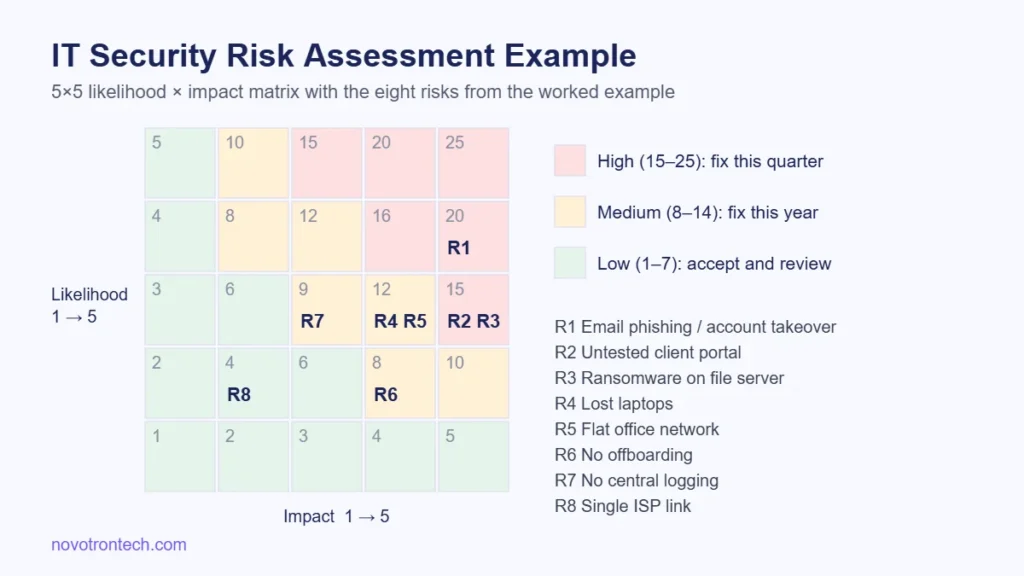
A worked IT security risk assessment example for a 60-person Noida firm: assets, threats, a 5×5 likelihood and impact matrix, the full risk register and the treatment plan.
A practical guide to AI development for Indian businesses: use cases that work, how AI projects are costed, and the DPDP and governance points to design in from day one.
How custom software is priced in India in 2026: published hourly rate benchmarks, worked budgets in rupees, GST, and the running costs that start after launch.
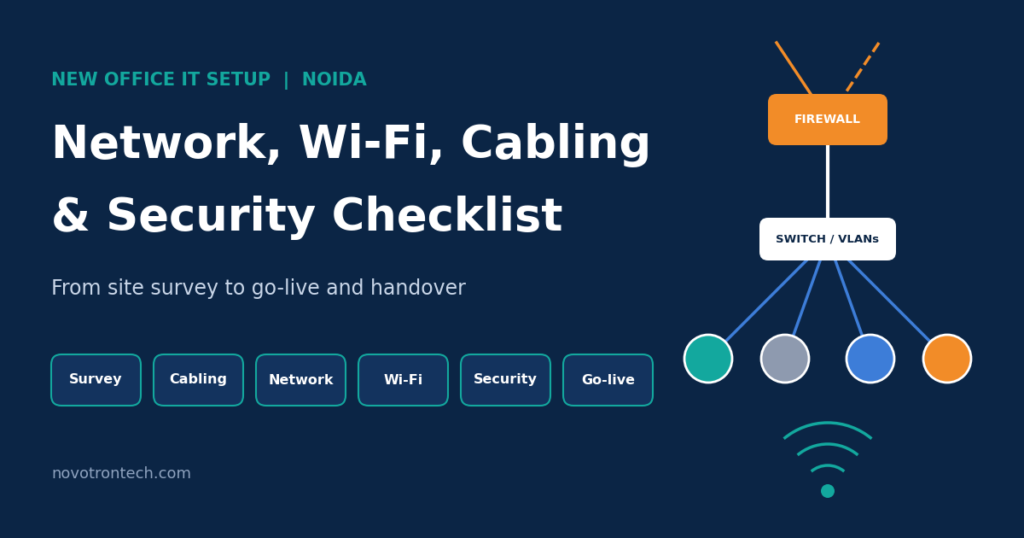
A practitioner’s checklist for setting up IT in a new Noida office: how the network fits together, phased steps from site survey to handover, success metrics, compliance points and common mistakes.
Firewall setup services for FortiGate, Sophos and Palo Alto explained: what a proper configuration includes, how traffic is processed, vendor fit, common mistakes and how to measure success.
A 25-step server hardening checklist for Windows Server and Linux, grouped into identity, network, patching, logging and data layers and mapped to CIS Benchmarks, NIST SP 800-123, ISO 27001 and the CERT-In Directions.
What a real penetration test includes, how the four phases work, what the report and retest must prove, and the six variables that drive the price in Delhi NCR.
When to bring an IT partner in, what the stack should look like at each headcount, what it costs in 2026, and how the first ninety days should run.
A nine-point scorecard, the questions that expose a weak vendor, a six-week timeline and the contract terms that matter before you sign.