Quick Answer: What ISO 27001 Certification Costs in India
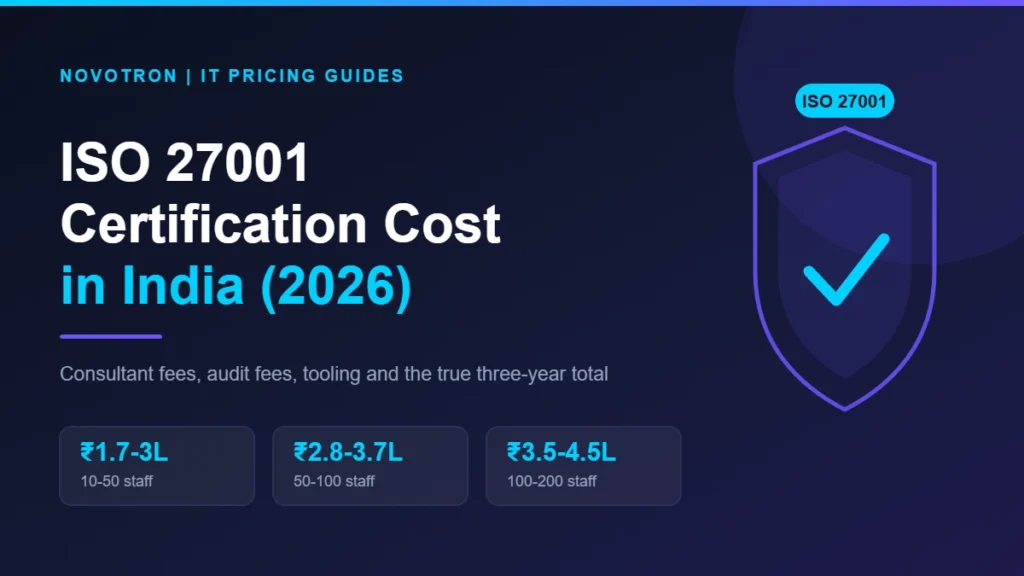
The ISO 27001 certification cost in India sits between ₹1.7 lakh and ₹4.5 lakh in year one for most small and mid-sized companies. A team of 10 to 50 people usually pays ₹1.7–3 lakh. A team of 100 to 200 people usually pays ₹3.5–4.5 lakh. In addition, that range covers consultant fees plus the certification body audit. Over three years, budget ₹4–6.5 lakh once you add surveillance audits, security tooling and your own team’s hours.
However, the headline number hides a lot. For instance, two companies of the same size can pay very different amounts. This guide breaks the ISO 27001 certification cost into its real parts, shows what pushes it up, and explains how to bring it down without weakening the certificate.
The ISO 27001 Certification Cost in India by Company Size
Furthermore, certification pricing in India follows headcount and scope. Consultants price on effort. Certification bodies price on audit days, and audit days follow the number of people and sites in scope.
| Company size | Consultant fee | Audit fee | Year-one total |
|---|---|---|---|
| 10–50 employees | ₹1–2 lakh | ₹70,000–1 lakh | ₹1.7–3 lakh |
| 50–100 employees | ₹2–2.5 lakh | ₹80,000–1.2 lakh | ₹2.8–3.7 lakh |
| 100–200 employees | ₹2.5–3 lakh | ₹1–1.5 lakh | ₹3.5–4.5 lakh |
| 200+ employees, multi-site | ₹4–8 lakh | ₹2–4 lakh | ₹6–12 lakh |
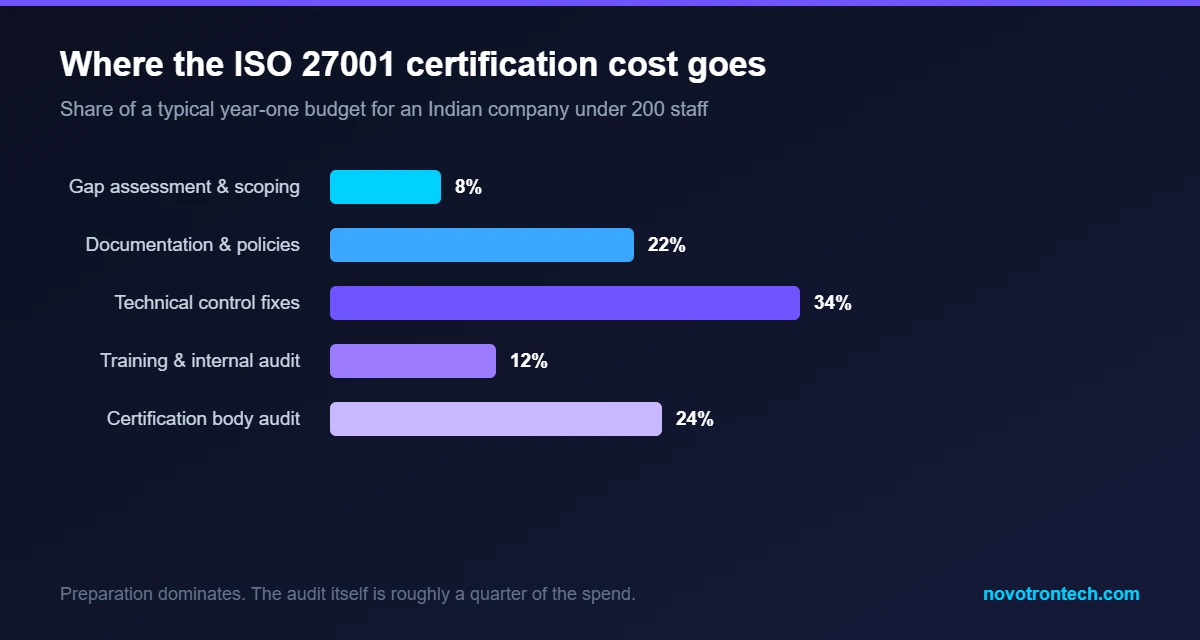
Notice that the audit fee stays relatively small. In fact, most of your ISO 27001 certification cost goes on getting ready, not on the audit itself. That is the part buyers consistently underestimate.
Where the ISO 27001 Certification Cost Actually Goes
To begin with, break any quote into five buckets. Because each one behaves differently, each one gives you a different lever to pull.
1. Gap assessment and scoping
First, a consultant maps what you already do against the standard. As a result, this takes one to two weeks. Consequently, a clean scope here saves money at every later stage. A vague scope is the single most common reason an ISO 27001 certification cost doubles.
2. Documentation and policy build
Next comes the paperwork: the information security policy, the risk register, the Statement of Applicability, and the supporting procedures. Altogether, expect two to three weeks. Templates help, but auditors spot a template that nobody adapted.
3. Technical controls
Then you close the technical gaps the assessment found. Typically that means access control, logging, backup testing, patching discipline and endpoint protection. Meanwhile, this is where firms with older infrastructure feel the cost most sharply.
4. Training and internal audit
After that, your staff need awareness training and you need one full internal audit before the certification body arrives. Budget 45 to 65 hours of your own team’s time, worth roughly ₹90,000 to ₹1.3 lakh in salary cost.
5. The certification audit
Finally the certification body runs Stage 1, a documentation review, followed by Stage 2, the on-site or remote evidence audit. After that, the certificate lasts three years.
The Ongoing ISO 27001 Certification Cost Nobody Quotes
In other words, the year-one figure is not the whole story. Since certification is a three-year cycle, plan for the full cycle from the start.
- Surveillance audits, years two and three: ₹60,000–80,000 each year.
- Security tooling: ₹95,000–1.5 lakh a year for password management, endpoint protection and log retention.
- Internal effort: evidence collection never stops. Someone owns it every month.
- Recertification in year four: ₹1.5–2.5 lakh.
Overall, add it up and the realistic three-year ISO 27001 certification cost lands between ₹4 lakh and ₹6.5 lakh for a company under 100 people. Larger or multi-site organisations should double that.
What Pushes Your ISO 27001 Certification Cost Up
In practice, five factors move the number more than anything else. Therefore, check each one before you accept a quote.
- Wide scope. Certifying the whole company costs far more than certifying one delivery unit. Many Indian firms certify the unit their clients ask about, then extend later.
- Multiple locations. Every extra site adds audit days. Remote audits help, but they rarely remove the cost entirely.
- Old infrastructure. Unsupported servers and flat networks force real spending before an auditor will pass you.
- No existing evidence. If nobody logs changes or reviews access today, you are building a habit, not just a document.
- Cloud sprawl. Undocumented SaaS accounts create risk you must first find, then govern.
On the other hand, companies that already run structured IT operations get through cheaply. If you already have monitoring, patch cycles and a service desk, much of the evidence exists. Our note on IT infrastructure monitoring explains why that trail matters.
How to Reduce the ISO 27001 Certification Cost Sensibly
Fortunately, you can cut the bill without buying a weaker certificate. In particular, these five moves work.
- Start narrow. Scope one business unit or one product. Extend at the first surveillance audit.
- Fix the basics first. Multi-factor authentication, tested backups and clean joiner-mover-leaver process remove many findings early. See our guide to multi-factor authentication.
- Train one internal lead auditor. A 40-hour course costs ₹15,000–45,000 and reduces consultant dependence every year after.
- Combine audits. If you also want ISO 9001 or SOC 2, run them together and share evidence.
- Negotiate the three-year cycle. Ask the certification body to price years one, two and three together rather than annually.
Above all, do not buy documentation alone. A folder of policies without working controls fails Stage 2, and a failed audit is the most expensive outcome available.
How Long It Takes, and When the ISO 27001 Certification Cost Lands
As a rule, most Indian companies reach certification in 12 to 16 weeks. A well-run organisation can do it in eight. A company starting from nothing usually needs six months.
| Stage | Typical duration | What happens |
|---|---|---|
| Gap assessment | Weeks 1–2 | Current controls mapped against the standard |
| Documentation | Weeks 3–5 | Policies, risk register and Statement of Applicability written |
| Technical controls | Weeks 6–8 | Access, logging, backup and endpoint gaps closed |
| Training and internal audit | Weeks 9–10 | Staff briefed, one full internal audit completed |
| Stage 1 and Stage 2 audit | Weeks 11–12 | Certification body reviews documents, then evidence |
| Certificate issued | Week 13–16 | Findings closed and certificate granted |
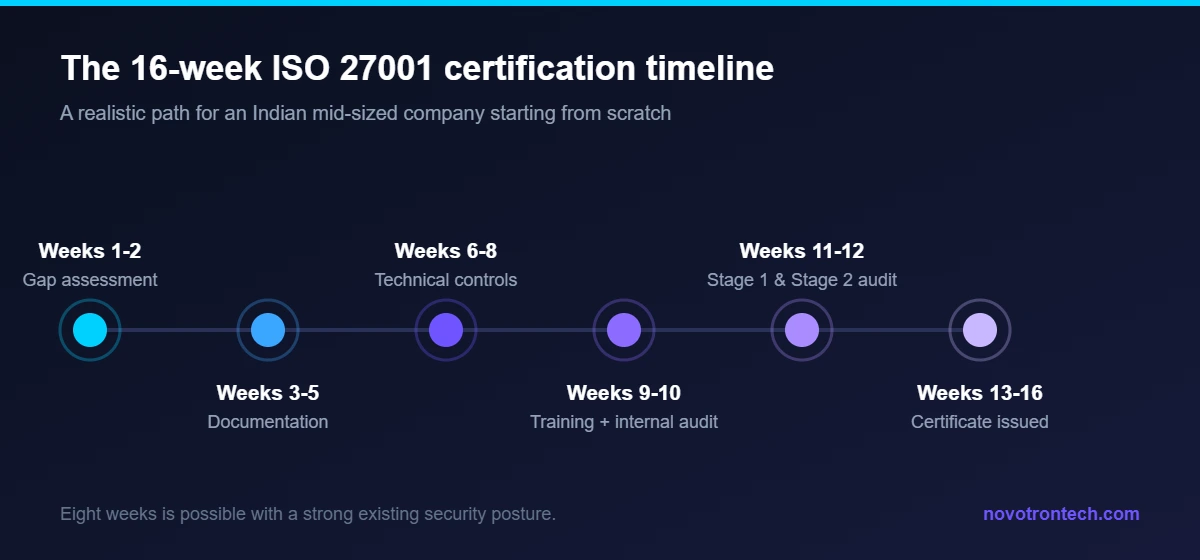
Therefore the honest planning answer is one quarter of focused effort, not one weekend. Equally important, book the audit early. Certification bodies in Delhi NCR get busy in the January and March quarters.
Why ISO 27001 Now Costs Less Than Ignoring It
Meanwhile, India’s regulatory position changed sharply. The Digital Personal Data Protection Rules were notified in November 2025, and enforcement of penalties begins in May 2027. Notably, the numbers are serious.
- Failure to protect personal data with reasonable safeguards: penalties reaching ₹250 crore.
- Failure to notify the Data Protection Board and affected individuals: penalties reaching ₹200 crore.
- CERT-In still requires incident reporting within six hours of noticing an incident.
An ISO 27001 information security management system does not grant legal immunity. Nevertheless, it produces exactly the evidence a regulator asks for: a risk register, access records, incident logs and a documented response process. Our DPDP Act compliance checklist and our guide to CERT-In compliance show how closely the two overlap.
Commercially, the case is simpler still. Enterprise buyers and overseas clients increasingly ask for the certificate before signing. For many Indian service companies, the ISO 27001 certification cost is smaller than a single deal lost to a security questionnaire.
ISO 27001 Certification Cost Versus Other Security Spend
Buyers often weigh certification against a penetration test or a monitoring contract. In truth, these solve different problems, and the price signals that.
| Investment | Typical India price | What it gives you |
|---|---|---|
| ISO 27001 certification | ₹1.7–4.5 lakh year one | A governance system plus a certificate buyers recognise |
| VAPT engagement | ₹60,000–5 lakh per scope | Proof of specific technical weaknesses |
| Cyber security audit | ₹50,000–3 lakh | A point-in-time view of control health |
| SOC as a service | ₹250–900 per endpoint monthly | Continuous detection and response |
Ideally you sequence them. Fix the basics, certify the system, then add monitoring. Buying monitoring first while access control stays broken simply produces alerts nobody can act on.
What the Auditor Checks, and Where the ISO 27001 Certification Cost Sits
ISO 27001:2022 groups its controls into four themes, as published by the International Organization for Standardization. Knowing them helps you predict where your ISO 27001 certification cost will concentrate.
- Organisational controls. Policies, supplier management, incident process and asset ownership. Mostly effort, not spend.
- People controls. Screening, awareness training, disciplinary process and remote-working rules. Cheap, but often neglected.
- Physical controls. Server room access, clear desk practice and secure disposal. Usually modest for an office-based firm.
- Technological controls. Access management, cryptography, logging, malware defence, backup and secure development. This is where real money goes.
Consequently, a company with tidy technology and messy paperwork pays less than the reverse. Documents can be written in weeks. Rebuilding an unpatched estate cannot.
Choosing a Consultant Without Inflating the ISO 27001 Certification Cost
Unsurprisingly, consultant pricing in India varies widely for the same deliverable. Accordingly, ask four questions before you sign.
- Will you implement, or only advise? Advice-only engagements look cheap, then leave your team doing the technical work anyway.
- Who writes the risk register? If the answer is you, the fee should drop accordingly.
- Is the certification body fee included? Many quotes exclude it. Always ask for the combined ISO 27001 certification cost.
- What happens at the surveillance audit? Ongoing support should be priced now, not negotiated later under pressure.
Additionally, be wary of anyone promising certification in four weeks. Auditors expect evidence that controls have actually operated, and evidence needs time to accumulate.
Mistakes That Inflate Your ISO 27001 Certification Cost
In our experience, we see the same four errors repeatedly, and each one adds real money.
Certifying everything at once
Above all, scope creep is the biggest single cost driver. Start with the unit your clients ask about. Extend later, when the system already runs.
Treating it as a documentation project
Unfortunately, policies alone fail Stage 2. Auditors sample evidence, so they ask to see actual access reviews and actual backup tests.
Leaving the internal audit until the end
An internal audit exists to find problems while fixing them is still cheap. Rushing it simply moves those findings into the certification audit.
Ignoring suppliers
Similarly, your cloud providers and IT vendors sit inside your scope. Gathering their assurances late delays the audit and sometimes forces a reschedule fee.
A Worked Example: One Noida Company’s ISO 27001 Certification Cost
For example, consider a 70-person software services company in Noida. It runs Microsoft 365, two cloud environments and a small office network. Although it has backups, nobody tests them. Access reviews happen informally.
Its ISO 27001 certification cost worked out at ₹3.2 lakh in year one: ₹2.2 lakh for consulting and implementation support, and ₹1 lakh for the certification body. Separately, it spent ₹1.1 lakh on password management and endpoint licences. Internal effort came to roughly 55 hours across four people.
Year two added ₹70,000 for the surveillance audit plus the same licence renewal. In short, the first year carried the weight and later years settled into a predictable run rate.
ISO 27001 or SOC 2? Which One Indian Buyers Ask For
Certainly both prove security maturity, yet they suit different markets. Instead, choose by customer, not by preference.
European, Middle Eastern and Indian enterprise buyers usually ask for ISO 27001. It is a certification against an international standard, and procurement teams recognise the mark instantly. American buyers, especially technology companies, more often ask for SOC 2. That is an attestation report written by an accountant, not a certificate.
On price, the two land close together in India. A first SOC 2 Type II report commonly runs ₹8–15 lakh once readiness and the observation window are included, which makes the ISO 27001 certification cost look modest by comparison. Many Indian firms therefore certify to ISO 27001 first, then reuse most of the same evidence for SOC 2 later.
What to Prepare Before You Ask for a Quote
Naturally, you will get sharper pricing if you arrive with facts. So gather these seven items first.
- Headcount inside the intended scope, not the whole company.
- A list of physical locations and whether staff work remotely.
- Your cloud and SaaS inventory, including anything a single team bought alone.
- Whether you already run tested backups and how often you restore them.
- How access is granted and removed when people join or leave.
- Any existing certifications, client audits or security questionnaires you have completed.
- Your target date, and what is driving it.
With that pack in hand, a competent consultant can quote in days rather than weeks. Vague briefs produce padded quotes, because the consultant prices the uncertainty.
A quick reality check on any ISO 27001 certification cost quote
To that end, divide the total ISO 27001 certification cost by the number of people in scope. For a company under 200 staff, most reasonable year-one quotes land between ₹3,000 and ₹6,000 per person in scope. Anything far outside that band deserves a question.
The Bottom Line on Your ISO 27001 Certification Cost
First of all, treat certification as an operating commitment, not a one-off purchase. Specifically, year one carries the heaviest ISO 27001 certification cost because you are building a system that did not exist. Years two and three cost far less, provided somebody owns the evidence every month.
Above all, scope tightly, fix the technical basics before you write policies, and price the full three-year cycle up front. Companies that do those three things rarely feel surprised by the bill. Companies that skip them almost always do.
Frequently Asked Questions
What is the ISO 27001 certification cost in India for a 50-person company?
Budget ₹2.8–3.7 lakh in year one. That splits into roughly ₹2–2.5 lakh of consultant effort and ₹80,000–1.2 lakh of certification body audit fees. Add surveillance audits of ₹60,000–80,000 in each of the next two years.
Is ISO 27001 certification mandatory in India?
No. No Indian law requires it. However, client contracts often do, and the DPDP Rules expect reasonable security safeguards that an ISO 27001 system happens to document well.
How long does ISO 27001 certification last?
Three years. You must pass a surveillance audit in year two and year three, then a full recertification audit in year four.
Can a startup afford ISO 27001?
Yes, if the scope stays tight. A 15-person product company certifying one platform can finish near ₹1.7–2.2 lakh. Scope discipline matters far more than headcount.
Does the ISO 27001 certification cost include security tools?
Usually not. Consultant and audit quotes cover advice and assessment. Licences for password management, endpoint protection and log retention add roughly ₹95,000–1.5 lakh a year.
What happens if we fail the Stage 2 audit?
You receive nonconformities and a window to close them, commonly 60 to 90 days. Minor findings rarely cost extra. Major findings usually trigger a follow-up audit and a further fee.
Who issues ISO 27001 certificates in India?
Accredited certification bodies do, not consultants. Always check the accreditation mark on the certificate. An unaccredited certificate will not satisfy a serious enterprise buyer.
Planning Your Certification Budget
Novotron helps Indian businesses close the technical gaps that drive the ISO 27001 certification cost upwards, from access control and logging to backup testing and endpoint hardening. We work from our office at Aycon Tower, Sector 135, Noida, with clients across Delhi NCR and the rest of India. To scope your own position, see our compliance and audit services, read more IT pricing guides, or call +91-8130009878. You can also email sales@novotrontech.com.